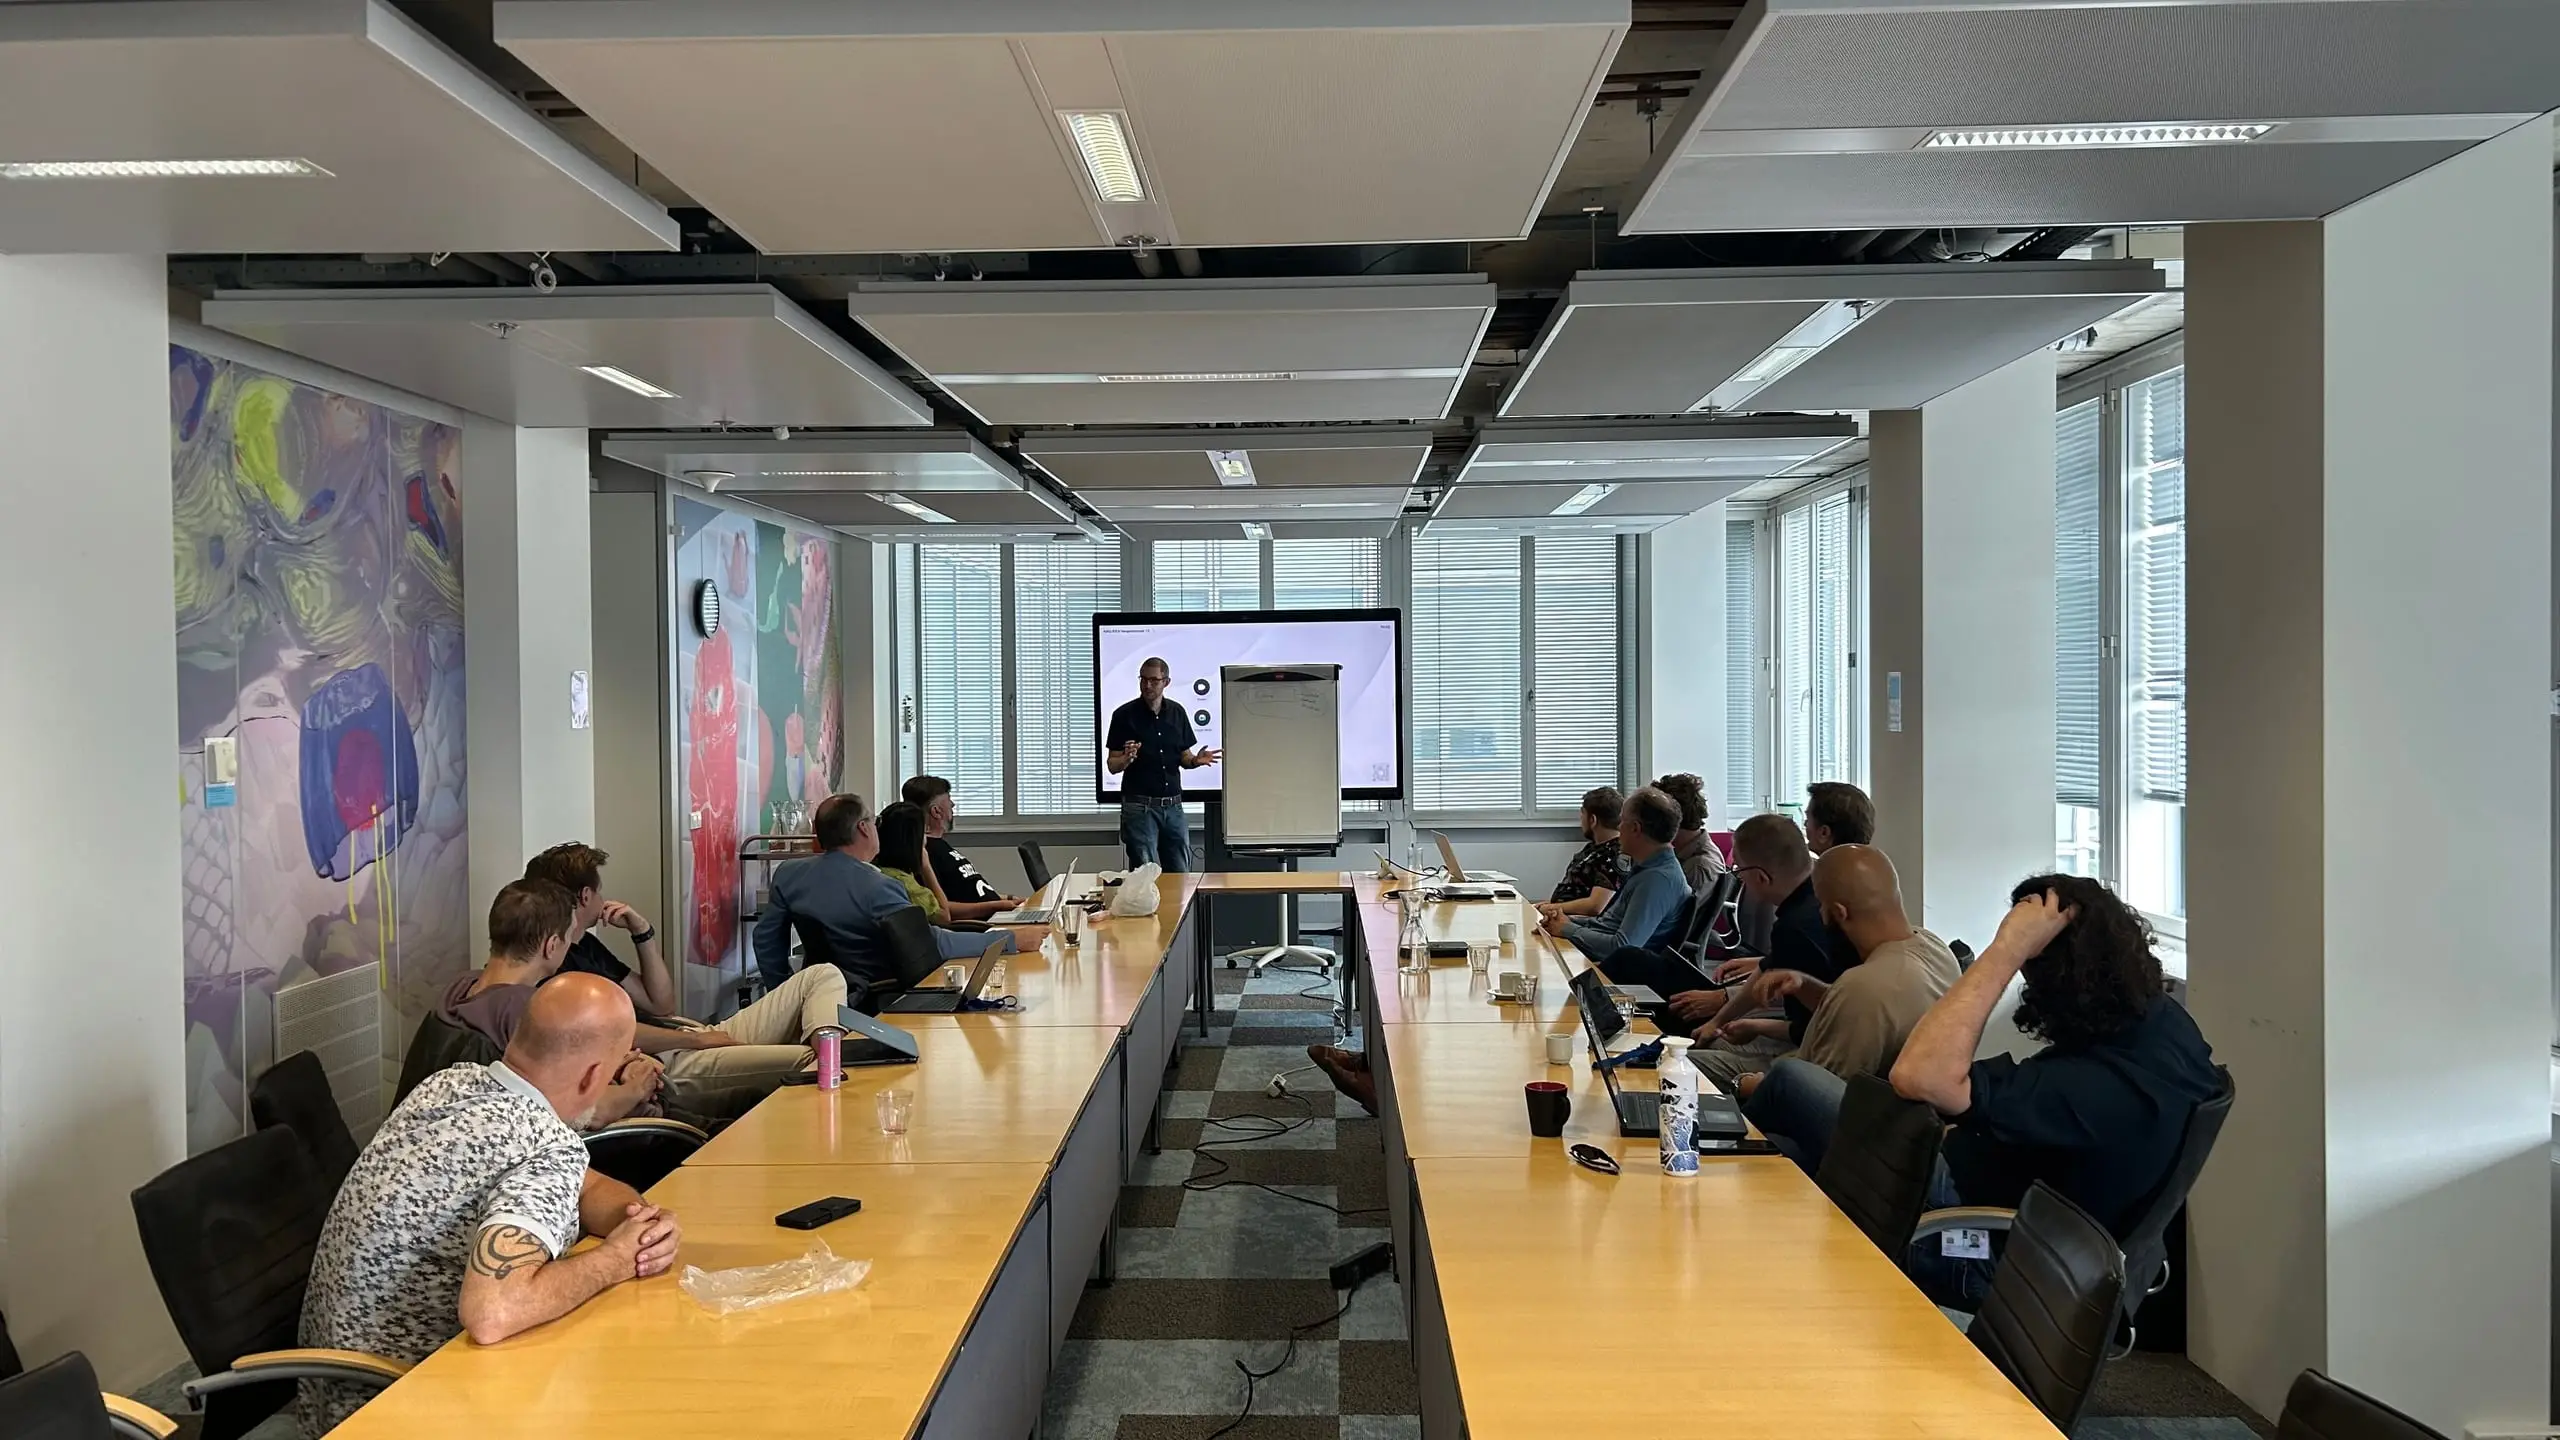
The DAWO community is an open platform where government, industry, and society collaborate to build a digitally autonomous workplace. It provides a shared space for public and private entities to work together on building blocks that can be inspected and replaced.